Enter Global Markets With Nomius

Our mission is to make compliance accessible, affordable, and continuous. Nomius transforms compliance from a barrier into an enabler of innovation.

Start with a compliance assessment, and we add the framework each of your markets needs

We support: GDPR, NHS, ISO, HIPAA, NIST and Cyber Essentials badges See all frameworks
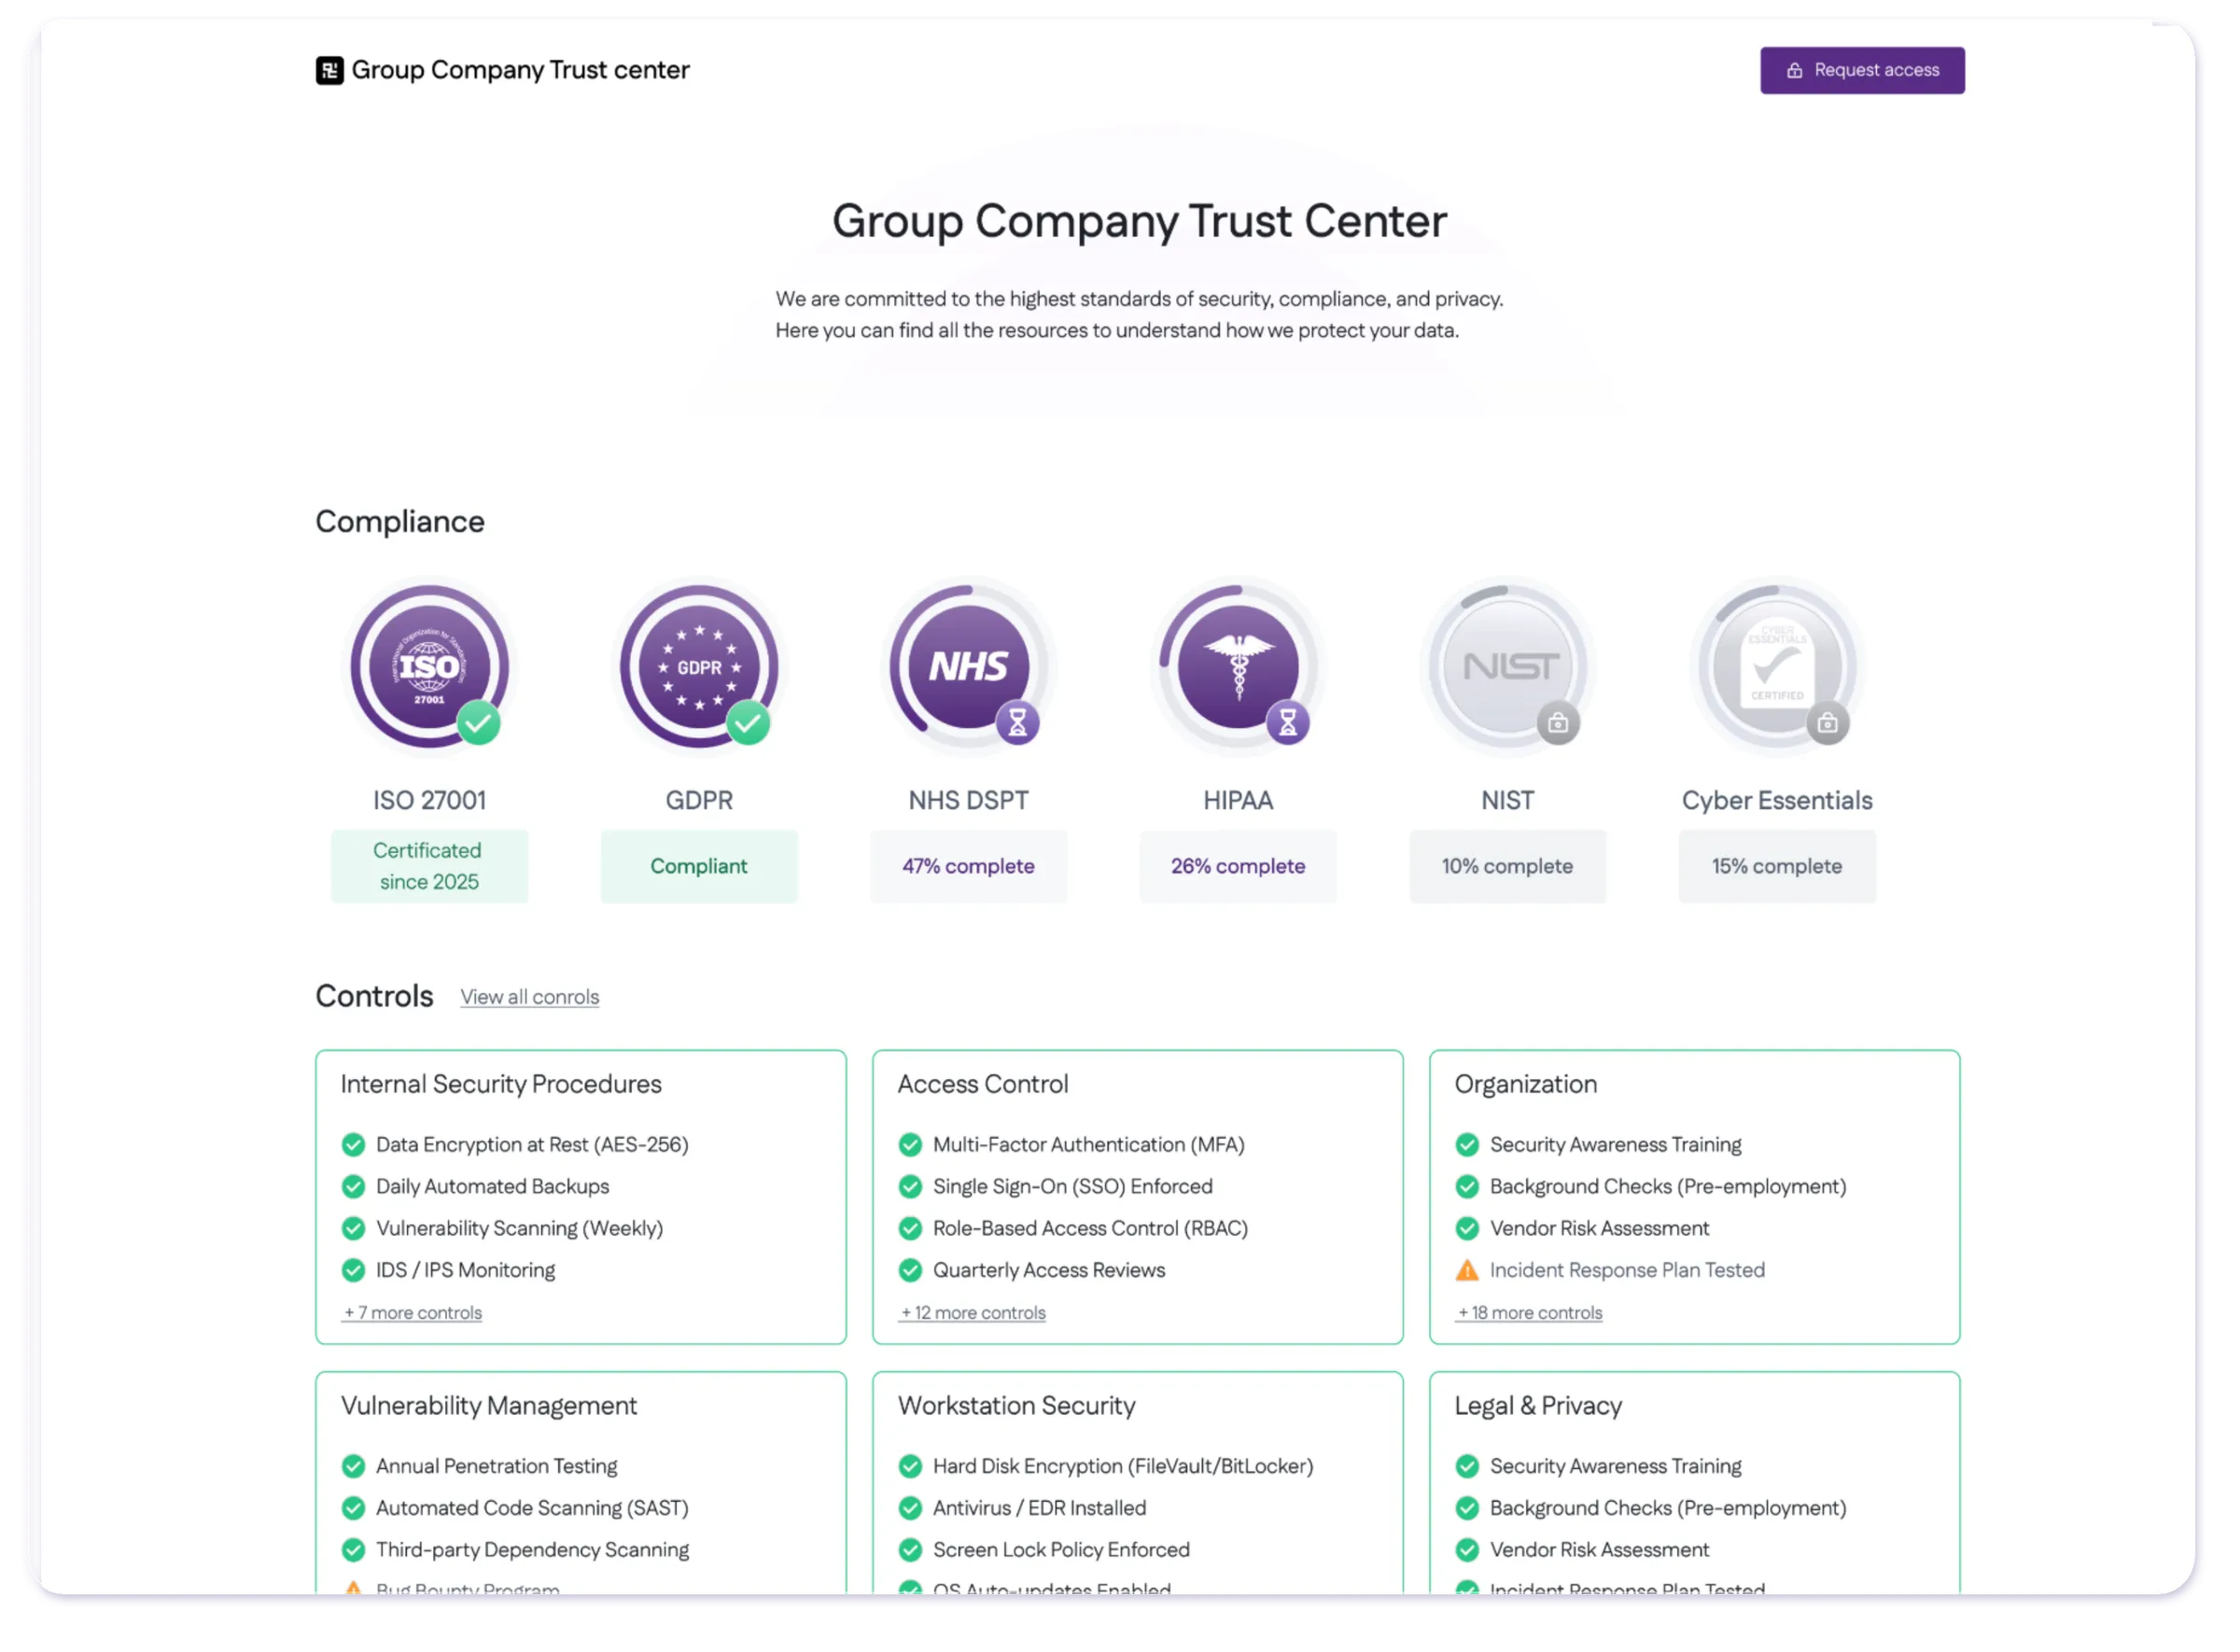
The Nomius Trust Center: compliance status for ISO 27001, GDPR, NHS DSPT, HIPAA, NIST and Cyber Essentials, and internal controls
We support: GDPR, NHS, ISO, HIPAA, NIST and Cyber Essentials badges See all frameworks

Trusted by our Partners

Join companies already growing

You've built a product people want
Now compliance blocks your go-to-market?

One workflow for your quality, privacy and security work

Meet Regulatory Compliance Obligations Across International Markets with Nomius

Quality and product lifecycle standards, data privacy, cybersecurity and AI governance in one platform, and we add the framework your market needs.

Multi-Market Compliance Assessment

Start with a compliance assessment, then work with our regulatory team on your QMS, technical file and compliance frameworks

  • One compliance assessment
  • Cross-mapped controls, so evidence collected once counts for every framework it satisfies
  • A regulatory strategy and route, set with our team
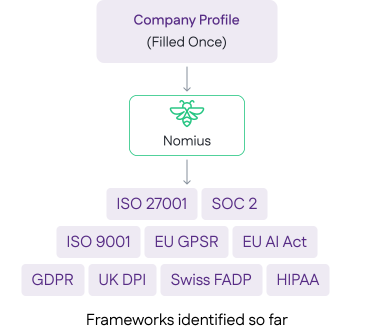
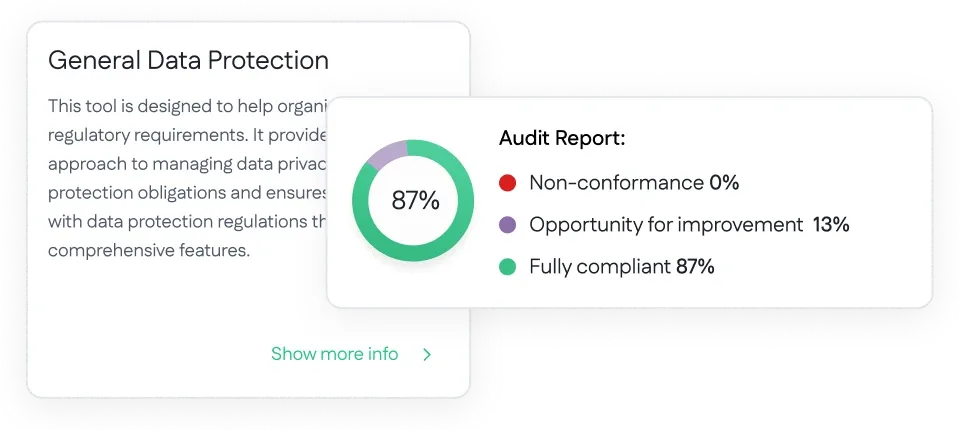
Illustration of a Nomius compliance assessment with examples of compliance frameworks

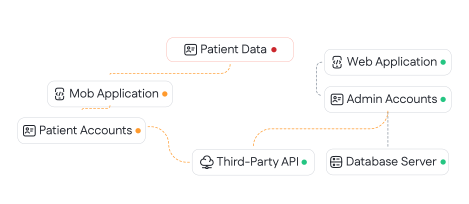
Global Data Privacy and Protection

Learn more: Global Data Privacy and Protection

One solution for multi-market compliance:

  • GDPR
  • UK DPA
  • Swiss FADP
  • HIPAA
  • ISO 27701
  • Managing cross-border data protection obligations
  • Automating compliance workflows and documentation
  • Monitoring regulatory changes across jurisdictions
  • Showing each control's status and its evidence
  • Maintaining detailed audit trails
  • Streamlining privacy impact assessments
  1. Nomius
  2. Receive ready to sign policiesSign with e-Signature
  3. Monitor the controlswith evidence collected
  4. Run the auditbuilt into Nomius
  5. Show your evidence
    to the auditor

Cybersecurity Governance

Learn more: Cybersecurity Governance

One solution for multi-market compliance:

  • ISO 27001
  • SOC 2
  • CIS
  • EU NIS 2
  • EU CRA
  • UK Cyber Essentials
  • Cross-domain security alignment
  • Certification readiness assessment
  • Security policy automation
  • Asset management
  • Each control's status with its evidence
  • Integrated risk management

Built-In Features to Manage Your Compliance Needs

Compliance work in one platform

  • Document e-signing
  • Audit
  • Incident Management
  • Risk Management
  • Training
  • Change Management
  • Document Control
  • Supply Chain Management
  • CAPA & Deviations
  • Project Design Control
  • Product File
  • Inventory Management
  • Customer Feedback and Complaints

Audit

Internal audit planning, execution and reporting, with AI assistance and the control evidence collected

A sample internal audit report in Nomius

Incident Management

Enables incident and near-miss reporting, tracking, and resolution to ensure timely responses to incidents and near-misses.

Incident Management

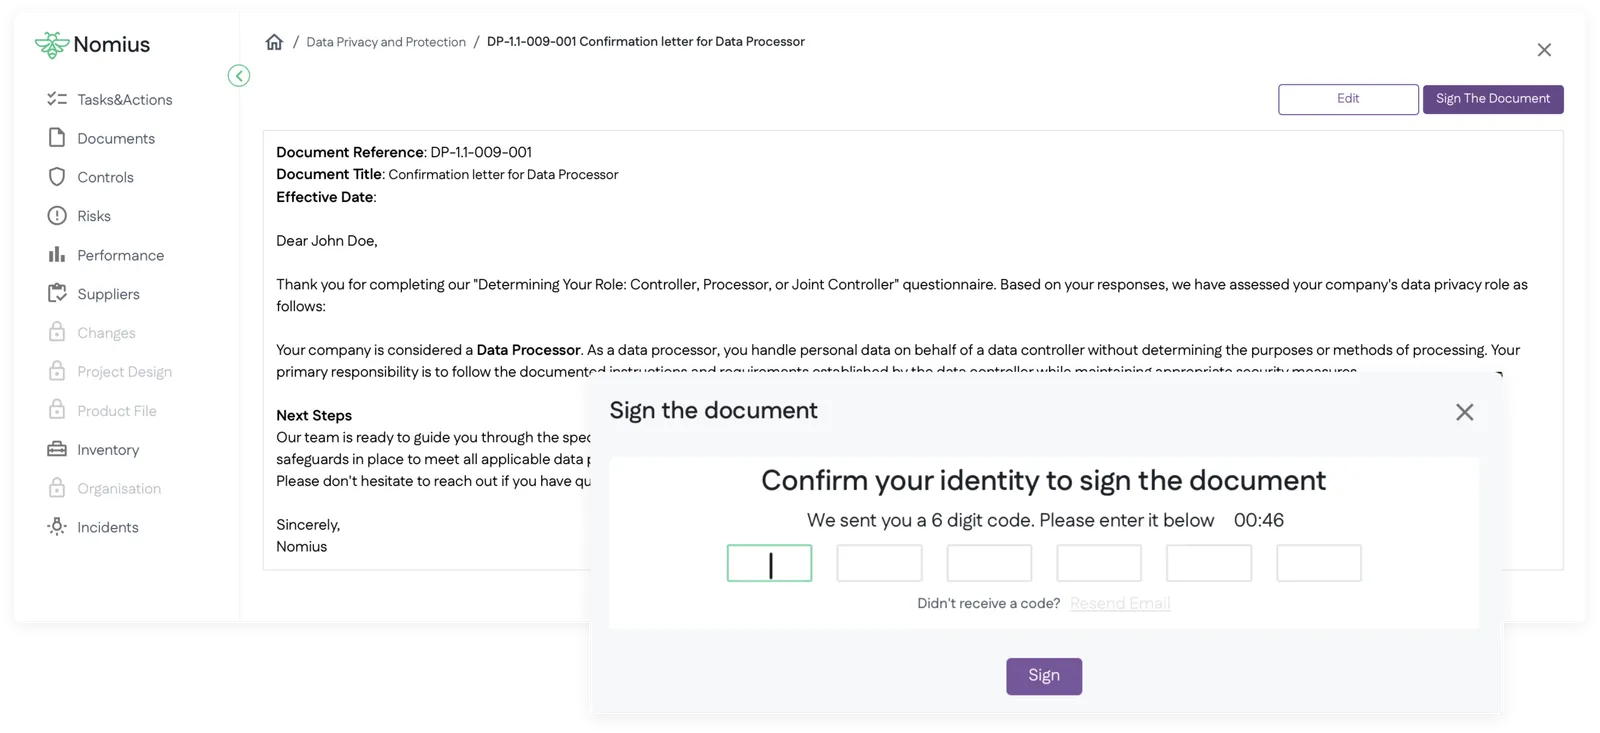
Two-factor e-Signature

Documents reviewed, approved and e-signed with two-factor authentication

Two-factor e-Signature

Not sure what compliance you need?
Ask our regulatory team

Join the Design Partner Programme. Tell us about your product and the markets you plan to enter, and we will show you where Nomius fits.

Get started

Our Services

Regulatory and quality consulting led by Nataliya Kuras, our co-founder, sold with the product when you need it, from regulatory strategy and technical files to audit preparation.

Global Compliance Frameworks

The frameworks page shows which are in Nomius and which we add for your market

Region
View all Frameworks
  • ISO/IEC 27001

  • Cyber Essentials Plus

  • NIST Cybersecurity

  • NHS DTAC

  • CIS Controls

  • NHS DSPT

  • NIS2 Directive

  • SOC 2

  • EU GDPR

  • UK GDPR

  • Swiss FADP

  • HIPAA

  • DPF

  • PIPEDA

  • POPIA

  • Law 25

  • PIPA

  • EU Data Act

  • LGPD

  • PDPA

  • DPDPA

  • POLAA

  • ISO 27701

  • ISO 27018

  • ISO 27017

  • HITRUST CSF

  • UK Cyber Essentials

  • NIS

  • EU Cyber Resilience Act

  • NIST CSF and NIST 800-53

  • CSA

  • PSTIA

  • FedRAMP

  • ISO 42001

  • EU AI Act

  • DHAF

  • NordDEC

  • DiGA

  • EU EHDS

  • EU GPSR

  • ISO 9001

  • ISO 13485

  • MDSAP

  • 21 CFR Part 820

  • ISO 14971

  • IEC 62304

  • IEC 82304

  • UK MDR 2002

  • EU MDR

  • EU IVDR

Ready to move faster and comply smarter?
Your route to market starts here

Join the Design Partner Programme. Tell us about your product and the markets you plan to enter, and we will show you where Nomius fits.

Get started

Tell Us About Your Compliance Needs

Send us a message with any questions and our team will get back to you.

0 / 4000

Thank you. We will get back to you shortly.

We could not send that. Please check the fields and send again with JavaScript on, or email hello@nomius.io.